ldraw-nova: AI agents build LEGO models by writing Python geometry
In ldraw-nova, models write a plan and a Python generator instead of raw coordinates, but nothing checks physics or stability.
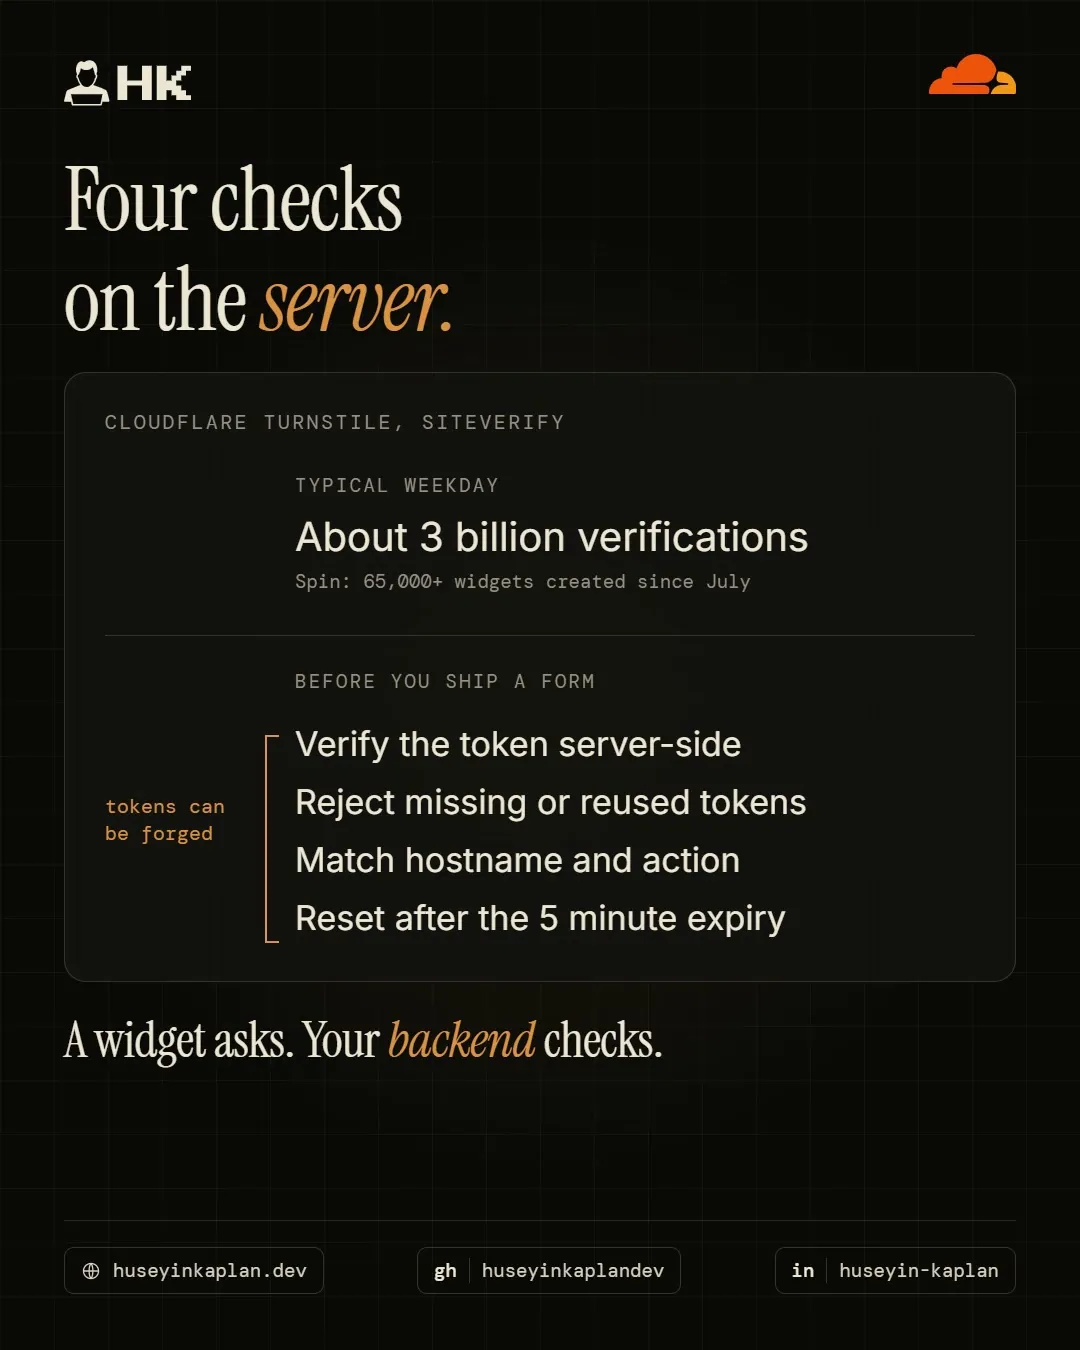
Turnstile tokens can be forged, so your backend must call Siteverify; Cloudflare now flags widgets that skip it with Fix with Spin.
A bot check on your signup form can render perfectly and still stop nothing.
Turnstile is two halves. The widget in the browser issues a token. Your backend sends that token to Siteverify. Skip the second call and a bot posts any string it likes. Cloudflare's own docs say tokens can be forged.
Cloudflare can now see that gap. It sees every widget and every Siteverify call, so a widget serving traffic with no backend check gets a "Fix with Spin" banner. Your own coding agent then proposes a plan, waits for approval, and wires the missing server step.
It's the half a generated app can skip without anything looking broken.
For any client-side check, confirm four things:
A widget asks the question. Your backend has to check the answer.
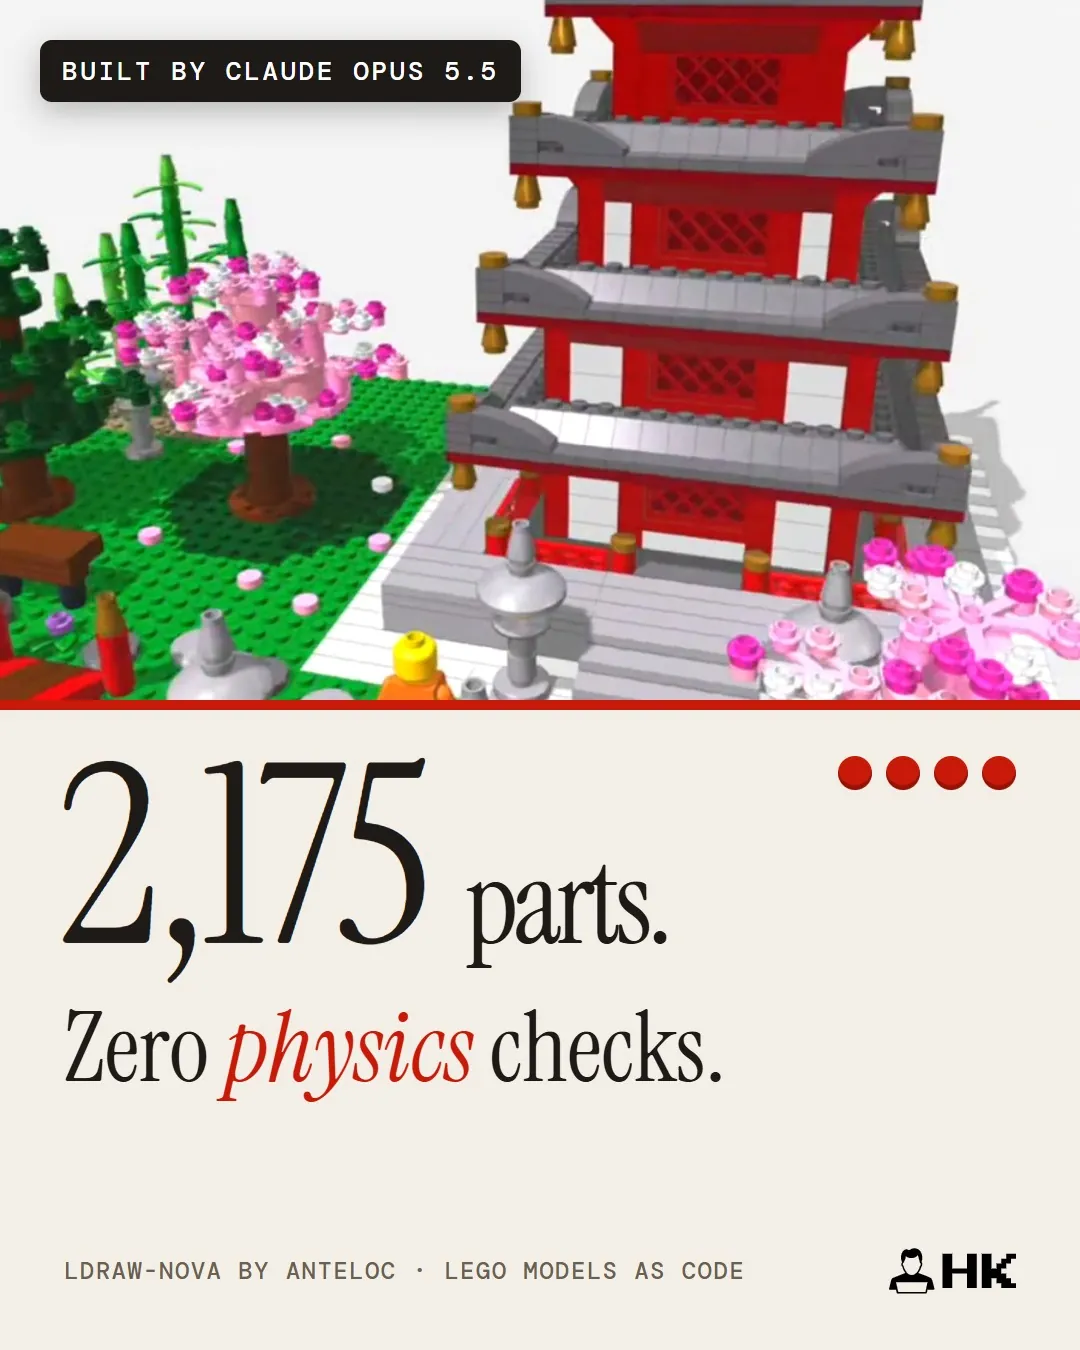
In ldraw-nova, models write a plan and a Python generator instead of raw coordinates, but nothing checks physics or stability.
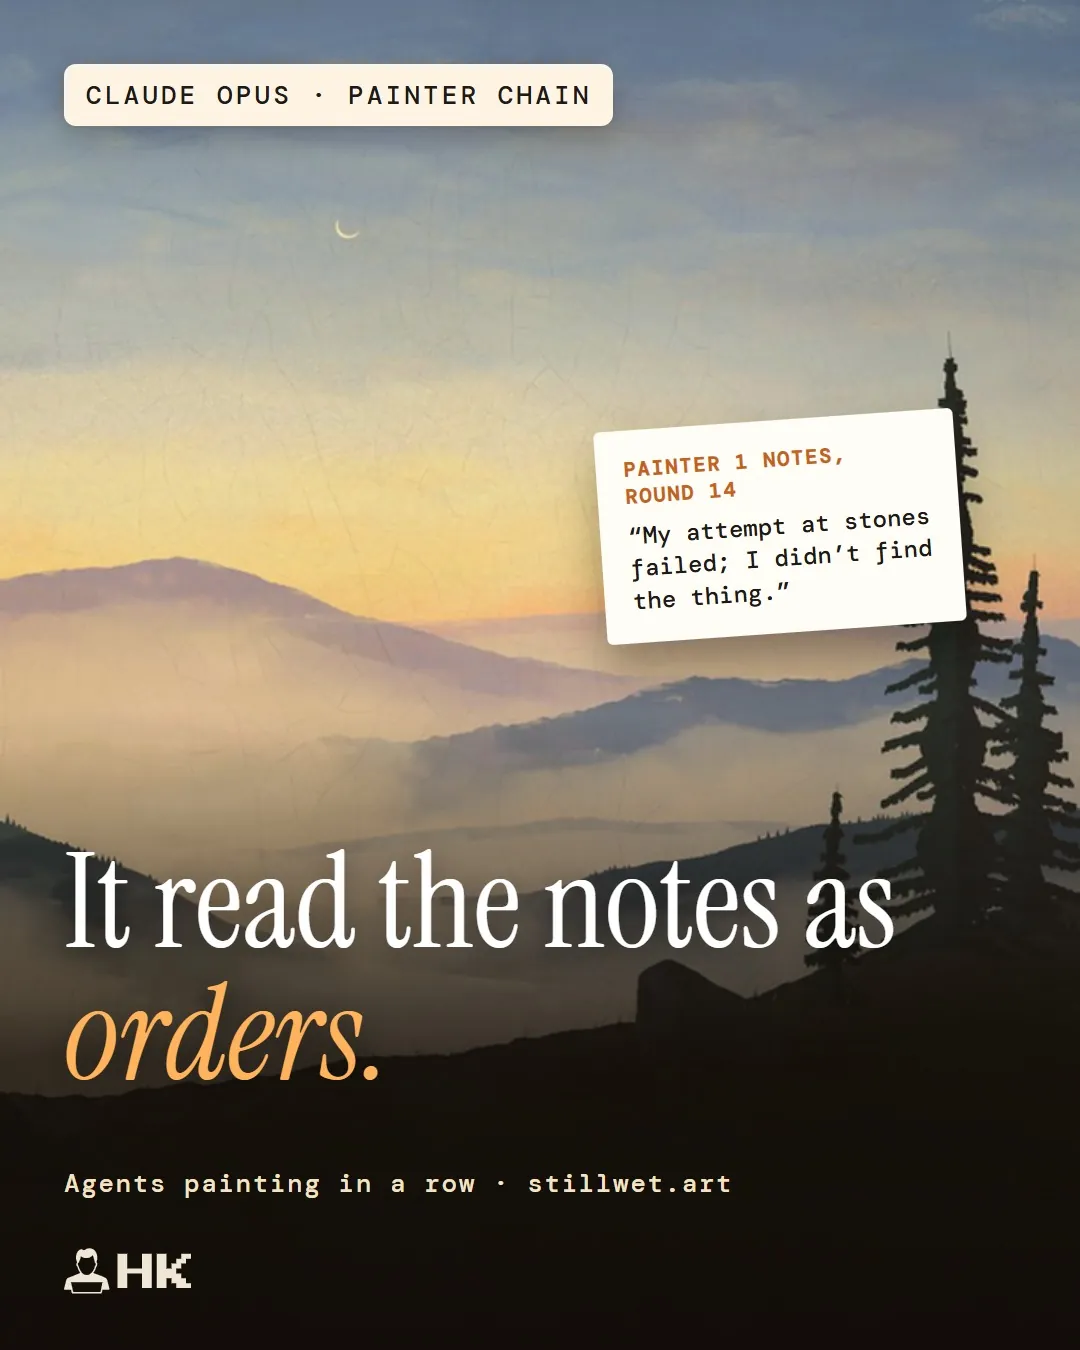
In stillwet's painter chains, Claude read earlier notes as instructions and missing notes failed silently, so label, log and verify agent handoffs.
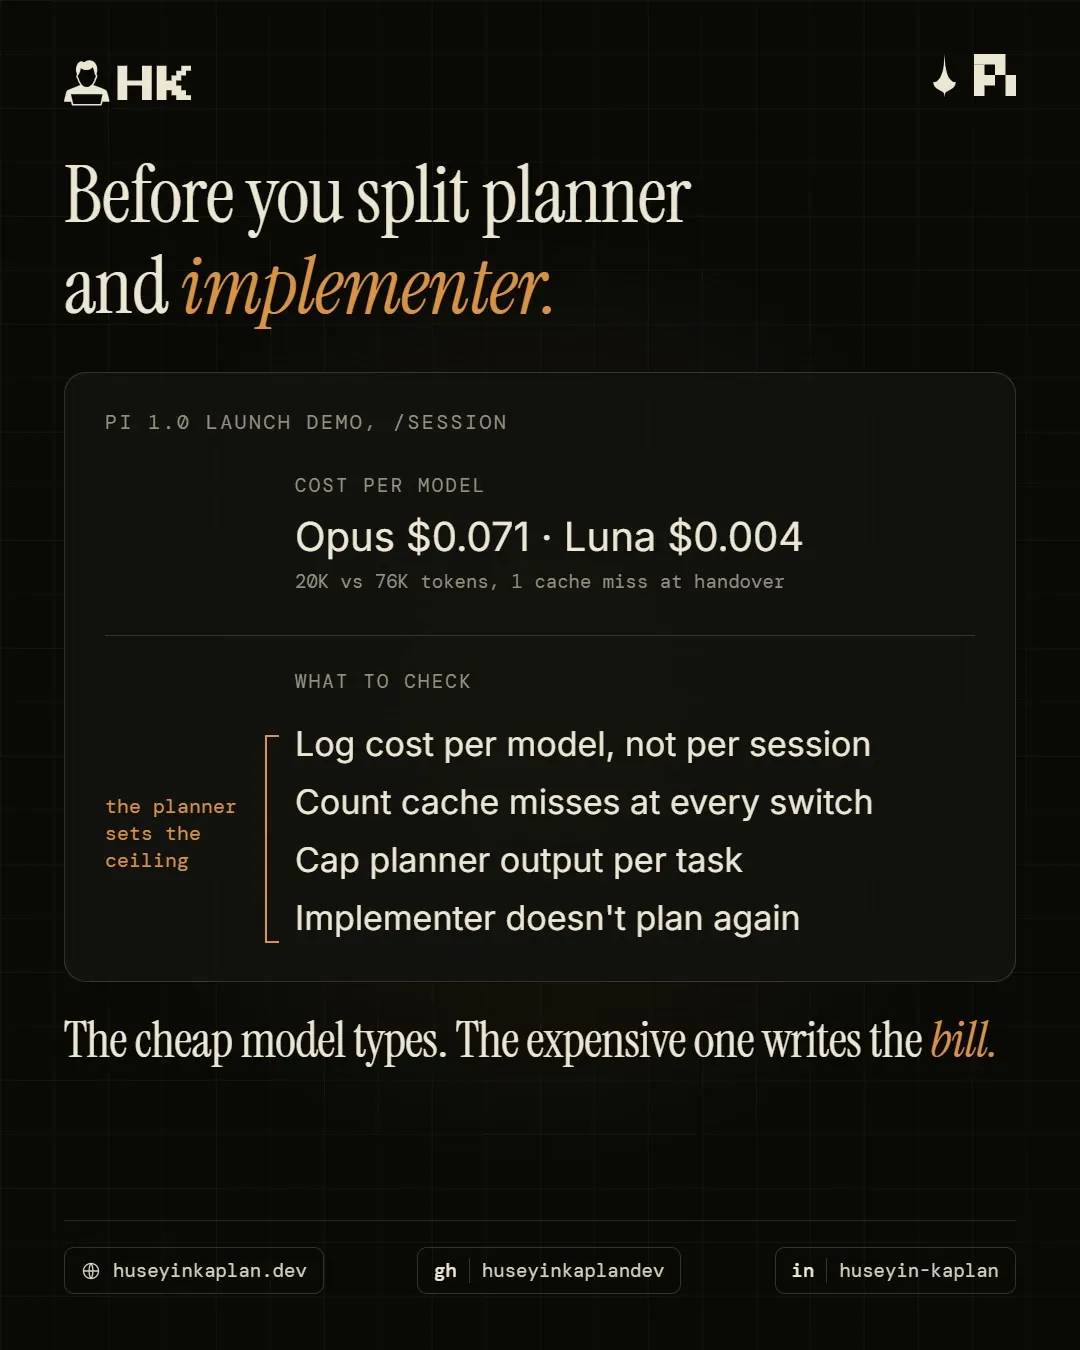
In Pi 1.0's demo, Opus used a fifth of the tokens yet cost 18x more than GPT 6 Luna, so log cost per model and count cache misses.